In distributed systems, network partitions, transient timeouts, and automated client retries make duplicate requests an inevitable operational reality. In mission-critical financial ledgers, e-commerce checkout funnels, and payment gateways (such as Stripe, Adyen, and PayPal), processing a request twice can cause catastrophic double-billing or inventory corruption. Designing robust distributed idempotency architectures ensures that executing an operation multiple times produces the exact same side-effect and outcome as executing it once.
1. Mathematical Definition of Idempotency in Computer Systems
In mathematics, an operation f is idempotent if applying it multiple times produces the identical result as applying it once:
f(f(x)) = f(x)
In RESTful HTTP protocol specifications:
- Naturally Idempotent Verbs:
GET,HEAD,PUT, andDELETEare designed to be idempotent. RepeatingDELETE /orders/123should result in order 123 being deleted, returning 200 or 204 consistently regardless of invocation count. Similarly,PUTreplaces the complete resource representation, meaning re-sending the same entity body leaves the resource in the identical state. - Non-Idempotent Verbs:
POSTandPATCHare fundamentally non-idempotent by default. CallingPOST /payments/chargethree times without idempotency guards will charge the customer three times, creating duplicate ledger entries and catastrophic reconciliation overhead.
2. Anatomy of Failure: The Network Timeout Dilemma
Consider a standard client-server interaction:
- The client sends a payment authorization request over the network.
- The server processes the payment successfully and records the transaction in the database.
- As the server attempts to transmit the
200 OKresponse back, a transient router partition drops the TCP packet. - The client experiences a 504 Gateway Timeout or TCP socket timeout.
From the client’s perspective, it is impossible to know whether the request failed before server execution or succeeded before the response was lost! The client’s automated retry engine (or an anxious user clicking ‘Pay Now’ repeatedly) fires a second identical request. Without distributed idempotency guards, duplicate side-effects occur.
This phenomenon is known as the Ambiguous State Problem. Because networks cannot guarantee instant acknowledgment, software systems must assume that every request transmitted across network boundaries may be delivered zero, one, or multiple times.
3. Idempotency Key Architecture: The Stripe Pattern
The gold standard for API idempotency is the Idempotency-Key Header Pattern popularized by Stripe.
The Request Lifecycle Workflow
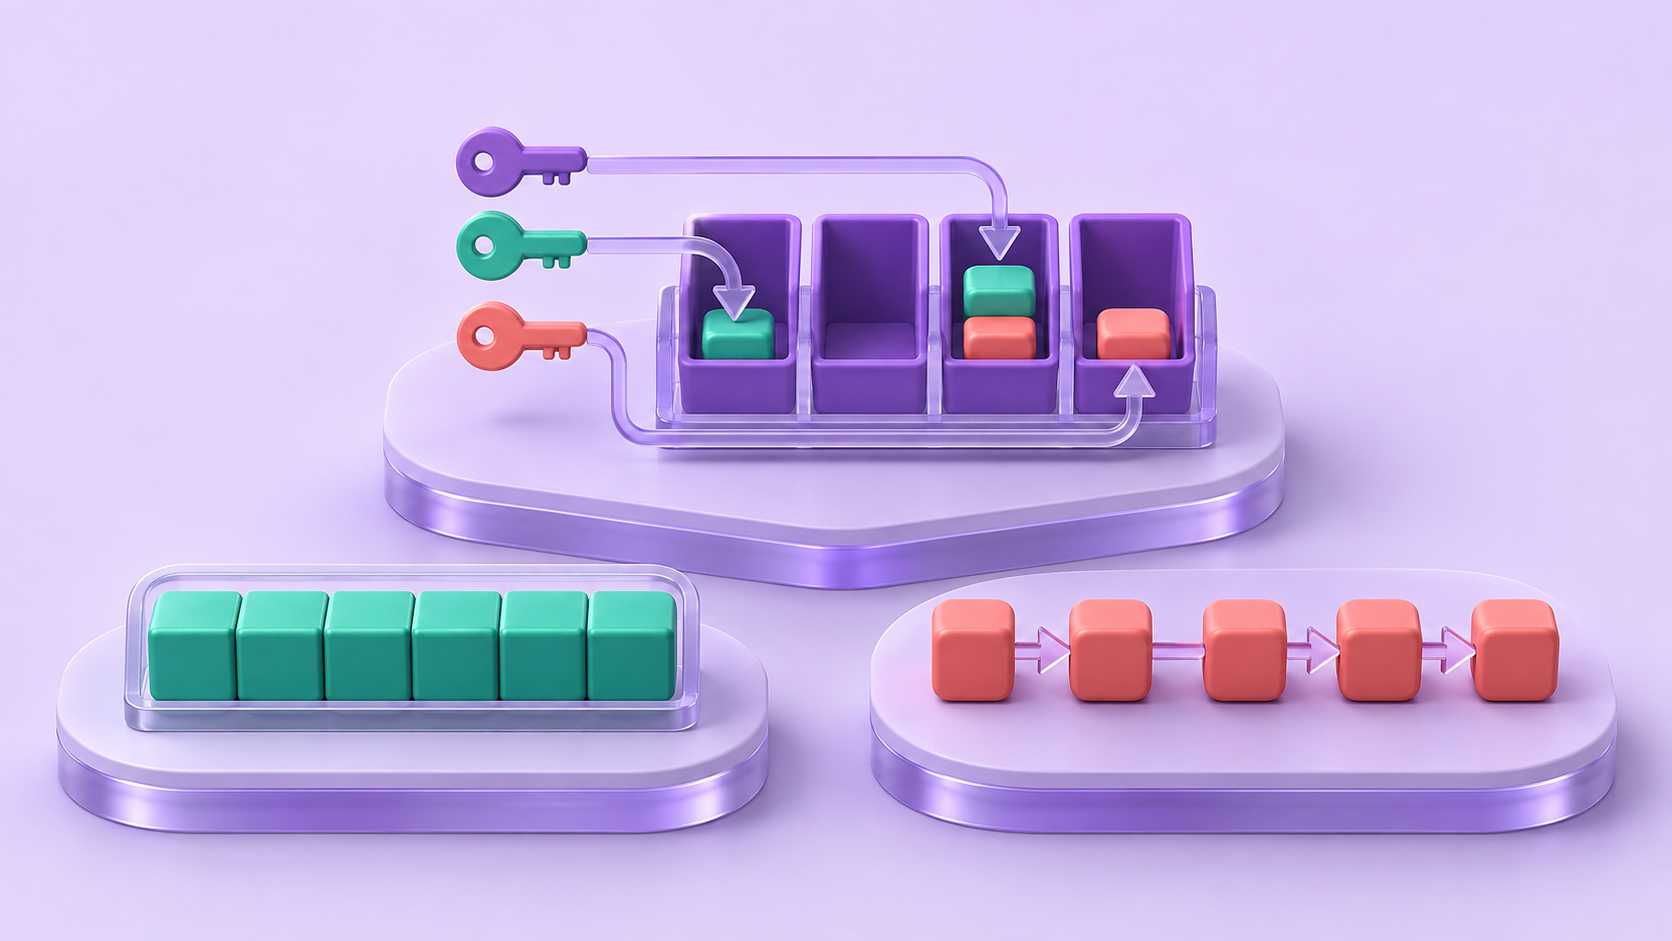
- The client generates a unique UUID v4 token (the
Idempotency-Key) and attaches it as an HTTP request header:Idempotency-Key: 7b8b2e1a-4c28-4f51-bfa6-123456789abc. - The API Gateway or service checks a distributed store (Redis or Relational DB) for the key.
- Scenario A (Key Not Found): The server acquires a distributed lease or inserts a record with status
PROCESSING. It executes the business logic, stores the response payload and HTTP status code in the idempotency table, updates status toCOMPLETED, and returns the response. - Scenario B (Key Exists & Status = COMPLETED): The server skips all business logic entirely and immediately returns the cached response payload and headers.
- Scenario C (Key Exists & Status = PROCESSING): A concurrent duplicate request is actively in-flight. The server returns
409 Conflictor holds the connection briefly until the primary execution finishes.
Payload Fingerprinting and Hash Verification
A critical vulnerability in naive idempotency implementations is key reuse with modified payloads. If an attacker intercepts or misconfigures a client that submits Idempotency-Key: K1 with amount = $10.00, and later submits Idempotency-Key: K1 with amount = $5,000.00, the server must not return the cached $10.00 response!
To prevent this, production systems compute a cryptographic SHA-256 fingerprint of the request payload (combining the URI path, HTTP verb, query params, and serialized JSON body) and store it alongside the idempotency record. If a subsequent request presents a matching key but an altered payload hash, the server immediately returns 422 Unprocessable Entity.
4. Database-Level Enforcement: Unique Constraints and Upserts
Software layers can fail, crash, or bypass cache tiers. True idempotency requires strict enforcement at the database storage engine layer:
- Unique Database Constraints: Add a unique index on
(tenant_id, idempotency_key). Any concurrent attempt to insert duplicate rows triggers an immediate unique key violation error (SQL Error 23505), preventing duplicate state creation. - Atomic Upsert Operations (ON CONFLICT DO NOTHING): Relational databases allow idempotent insert syntax that safely ignores duplicate attempts:
INSERT INTO orders (id, user_id, amount, idempotency_key) VALUES ('ord_1', 'usr_9', 99.00, 'idem_key_xyz') ON CONFLICT (idempotency_key) DO UPDATE SET updated_at = NOW(); - Optimistic Concurrency Control (OCC): Include a version integer or timestamp in update queries:
UPDATE accounts SET balance = balance - 100, version = version + 1 WHERE id = 123 AND version = 5. If another process modified the account in parallel, zero rows are updated, allowing the service to retry safely.
5. Distributed Transactions: Two-Phase Commit (2PC) Limitations
When mutations span multiple independent databases or microservices, traditional distributed systems attempted to maintain consistency using the Two-Phase Commit (2PC) protocol:
- Phase 1 (Prepare): A coordinator asks all participant nodes if they can commit the transaction. Participants write undo/redo logs and lock resources.
- Phase 2 (Commit): If all participants respond ‘YES’, the coordinator issues a global COMMIT command. If any node votes ‘NO’, the coordinator commands a global ROLLBACK.
Why 2PC Fails in Modern Cloud Scale: 2PC is a blocking protocol. If the coordinator crashes during Phase 2, participant nodes remain indefinitely locked, holding database row locks and starving all downstream transactions. Furthermore, 2PC severely degrades throughput across high-latency cross-region clouds, violating modern microservice availability targets (Brewer’s CAP Theorem).
6. The Transactional Outbox Pattern and Change Data Capture (CDC)
To achieve distributed consistency and idempotent event publishing without blocking 2PC locks, modern architectures deploy the Transactional Outbox Pattern.
The Dual-Write Problem
In microservices, a frequent anti-pattern is executing a database update and then publishing a message to Apache Kafka:
db.commit(); // Succeeded
kafka.publish(event); // Crashes before publish! Message lost forever!
Or conversely, publishing to Kafka first and having the database commit fail, creating phantom messages.
The Outbox Pattern Solution
- Instead of calling Kafka directly, the service writes the business entity AND an event record into an Outbox Table within the same local relational ACID database transaction:
BEGIN TRANSACTION;
  INSERT INTO orders (...) VALUES (...);
  INSERT INTO outbox_events (id, aggregate_type, payload, status) VALUES (...);
COMMIT;
- Because both writes share a single local database transaction, atomicity is guaranteed: either both are saved, or neither is.
- A dedicated background process—or a Change Data Capture (CDC) engine like Debezium reading the database write-ahead log (WAL)—asynchronously reads entries from the outbox table and streams them to Apache Kafka with guaranteed at-least-once delivery.
- Downstream consumers process the messages idempotently by tracking message IDs in their local deduplication stores.
7. Production Engineering Implementation: Idempotent Middleware in Python
Below is an enterprise-grade Python module demonstrating distributed idempotency management using atomic token verification, payload hashing, and cached payload responses:
8. Consumer Deduplication Patterns: Event-Driven Processing
In event-driven architectures utilizing Apache Kafka or RabbitMQ, brokers guarantee at-least-once message delivery. A message may be redelivered due to consumer crash restarts, network partitions during consumer offset commits, or rebalancing events.
To ensure idempotent consumer processing:
- Idempotent Business Logic: Prefer naturally idempotent operations. For instance, instead of
UPDATE inventory SET stock = stock - 1, issue an idempotent state update:UPDATE inventory SET status = 'RESERVED', reserved_by = 'order_456' WHERE order_id = 'order_456'. - Deduplication Table (Processed Messages): Every consumer database maintains a
processed_messagestable. When an event arrives with IDevt_789, the consumer executes the business mutation and recordsevt_789within the same local transaction. Ifevt_789already exists, the transaction aborts with zero side-effects. - Kafka Idempotent Producer & Transactions: At the broker level, Kafka’s idempotent producer assigns a Producer ID (PID) and sequence numbers to every message batch, automatically deduplicating broker-level network retries.
9. Frequently Asked Questions (FAQ)
Q: What is an Idempotency Key?
An idempotency key is a unique client-generated token (typically a UUID v4) passed in the request header. The server uses this key to recognize duplicate requests and return the original response without re-executing business logic.
Q: Why is the Transactional Outbox Pattern preferred over 2PC in microservices?
Two-Phase Commit (2PC) is a blocking synchronous protocol that causes high lock contention and catastrophic cascade failures across distributed networks. The Outbox pattern relies on local ACID transactions and asynchronous CDC streaming, preserving microservice isolation and high availability.
Q: What should an API return if a duplicate request arrives while the first is still processing?
The API should return HTTP 409 Conflict or HTTP 425 Too Early with a message indicating that a request with that idempotency key is currently being processed, instructing the client to wait before retrying.
Q: How long should idempotency keys be retained in cache?
Retention periods vary by business domain. Financial services typically enforce 24 to 72 hours of TTL, allowing clients to recover from day-long outages without risking duplicate charges. Cold keys can be archived in long-term audit tables.
Q: Can a GET request be non-idempotent?
By HTTP specification, GET must be safe and idempotent, meaning it does not alter server state. If an application increments a counter or executes a mutation inside a GET endpoint, it violates HTTP standards and can cause unintended mutations during browser prefetching or crawler indexing.
Q: What happens if a client reuses an idempotency key with a different request payload?
The server should calculate a cryptographic hash (SHA-256) of the initial request payload and store it alongside the key. If a subsequent request reuses the key with a modified payload, the server returns HTTP 422 Unprocessable Entity or 400 Bad Request to prevent payload spoofing.
Q: What is Change Data Capture (CDC)?
CDC is a software architecture that monitors database transaction logs (such as PostgreSQL WAL or MySQL Binlog) and automatically streams row-level inserts, updates, and deletes to an event broker like Kafka with zero application-level polling.
Q: How does a consumer achieve idempotency when reading from Apache Kafka?
Consumers track processed message IDs in a local deduplication table or database unique constraint within the same transaction that applies the message’s side-effects, ignoring messages whose IDs have already been processed.
Q: What is the difference between at-least-once and exactly-once delivery?
At-least-once delivery guarantees a message is delivered one or more times (duplicates possible). Exactly-once delivery is an end-to-end guarantee that a message produces side-effects exactly once, achieved by combining at-least-once transport with idempotent processing.
Q: How does Redis SET NX EX support idempotency?
Redis SET key val NX EX sets a key only if it does not already exist (NX) with an automatic expiration time (EX). This provides an atomic, distributed lock primitive to claim an idempotency key in a single sub-millisecond round-trip.
Q: What is optimistic concurrency control in idempotent updates?
Optimistic concurrency control tracks a version number on each record. Updates include WHERE version = current_version. If another worker updated the record concurrently, the version mismatch aborts the query cleanly without row locks.
Q: Why should clients generate UUID v4 for idempotency keys?
UUID v4 tokens provide 122 bits of cryptographic entropy, ensuring that two independent clients will never accidentally generate identical keys, preventing false-positive duplicate rejections.
10. Architectural Conclusion and Engineering Recommendations
Distributed idempotency is not an optional optimization; it is a foundational prerequisite for building dependable cloud architectures. When engineering distributed service interfaces:
- Mandate Idempotency-Key headers on all state-mutating endpoints (POST, PATCH) across payment, order, and billing APIs.
- Store Payload Hashes alongside Idempotency Keys to detect and reject fraudulent parameter alterations.
- Deploy the Transactional Outbox Pattern with CDC (Debezium/Kafka) to guarantee atomic event publishing without blocking 2PC locks.
- Enforce Unique Database Constraints as the ultimate physical safety barrier against concurrent race conditions.